
Construct log analytics query in log analytics workspace running in an emulated Azure environment.
", "tasks": "", "tasks_html": "", "published_date": "2020-04-07T18:00:00Z", "solutions": "Analyze virtual machine performance\n\nWhen you log in to Azure with the provided credentials, you will find an empty resource group. \n\n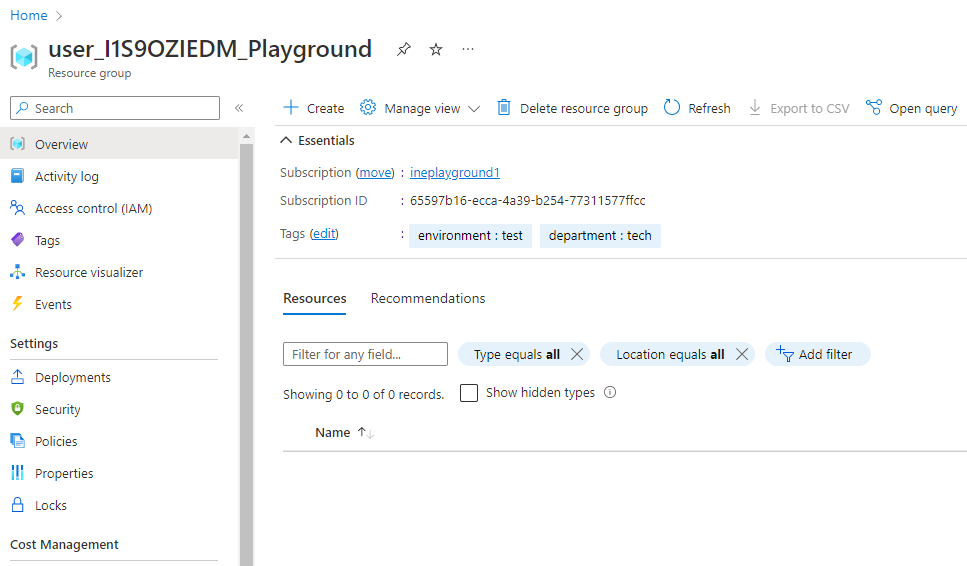\n\nThis lab uses the Log Analytics demo environment, which includes plenty of sample data that supports the sample queries.\n\nNavigate to the Log Analytics demo environment using the following URL.\n\n```\nhttps://portal.azure.com/#view/Microsoft_Azure_Monitoring_Logs/DemoLogsBlade\n```\n\n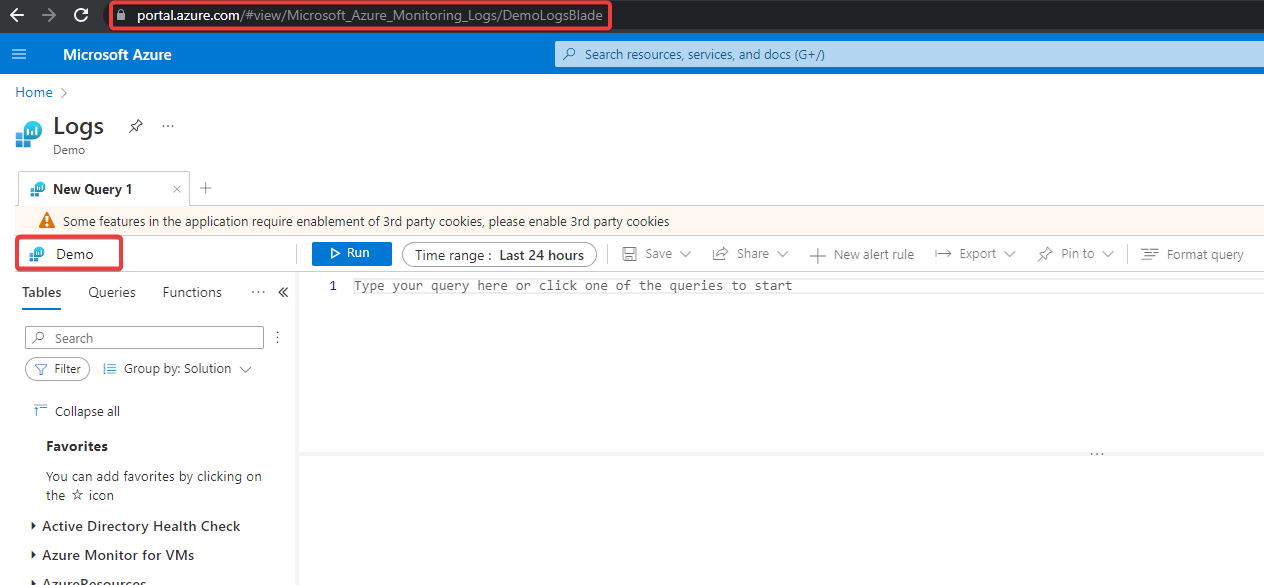\n\nConstruct a log analytics query that returns the following information:\n\n- Average Processor Queue Length performance counter data.\n- Aggregated every 30 seconds over the last hour.\n- Grouped by ComputerName.\n\nCopy and paste the log analytics query and click on **Run** by selecting the whole query.\n\n```\nPerf\n| where TimeGenerated > ago(1h)\n| where (CounterName == \"% Processor Time\" and InstanceName == \"_Total\")\n| project TimeGenerated, Computer, CounterValue\n| summarize avg(CounterValue) by Computer, bin(TimeGenerated, 1m)\n| where avg_CounterValue > 100\n| render timechart\n```\n\n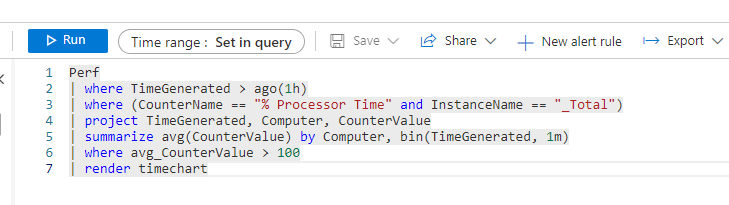\n\nTo view the results in a graph, select **Chart** on the results pane. Notice that there are various options for working with the chart, such as changing it to another type.\n\n\n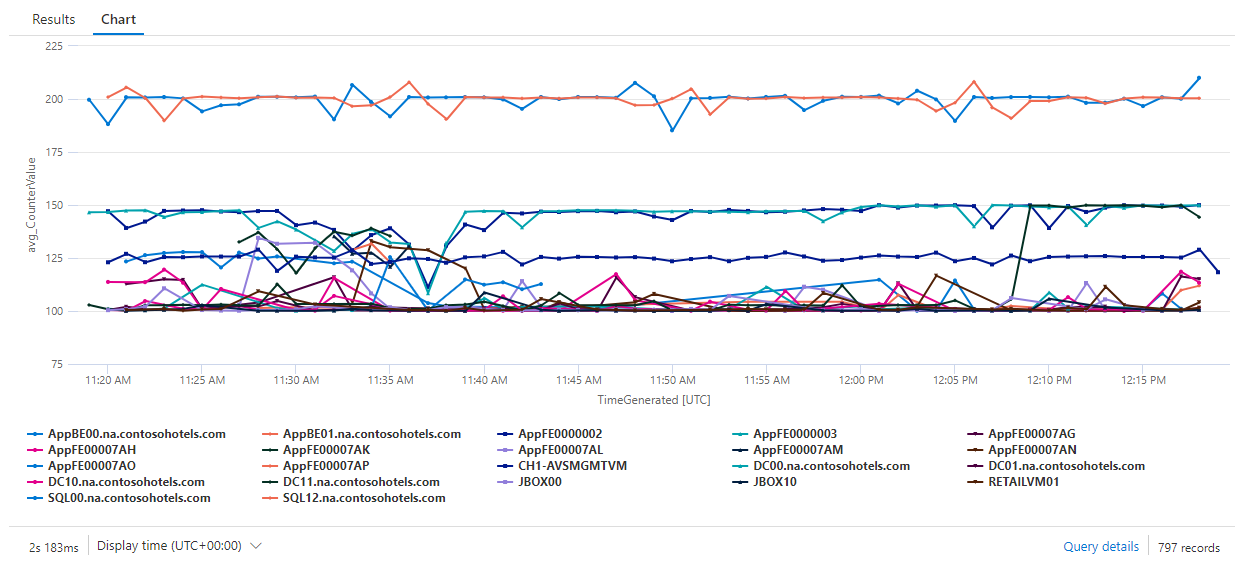\n\nClick on **Results** to view query results in a table organized by columns and rows.\n\n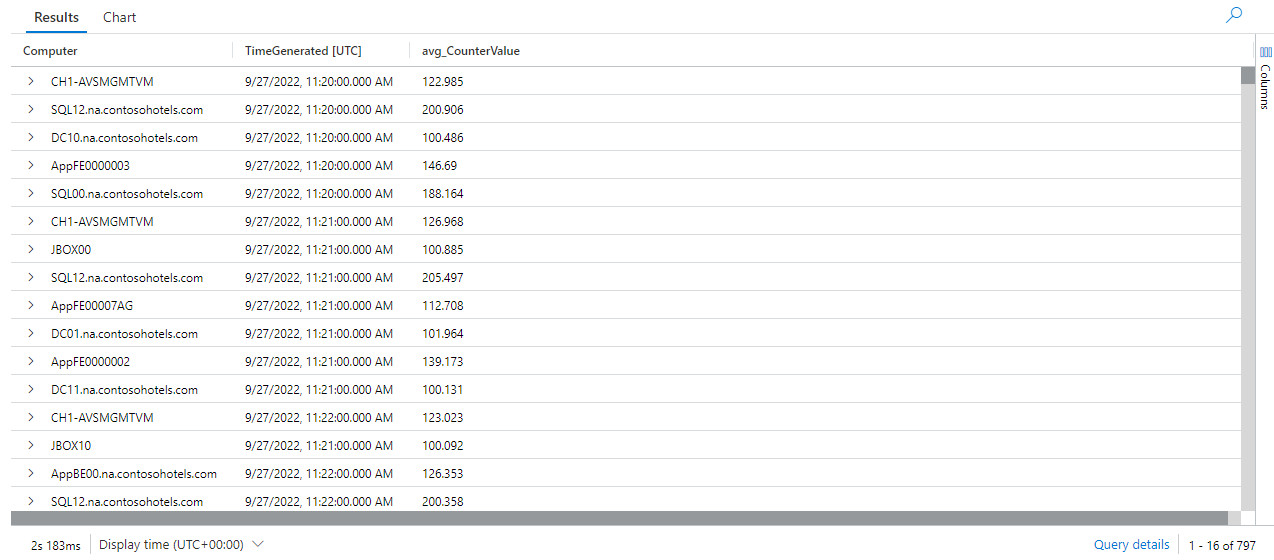\n\n# Search for diagnostic events\n\nConstruct a log analytics query that returns the following information:\n\n- Returns the computers with the most entries from the Event and SecurityEvent sources that contain the word \"Antimalware\".\n\nCopy and paste the log analytics query and click on **Run** by selecting the whole query.\n\n```\nsearch in (Event, SecurityEvent) \"Antimalware\"\n| summarize count(Computer) by Computer\n| top 10 by count_Computer desc nulls last\n```\n\n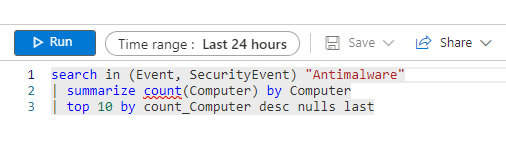\n\nThe result will provide the details about the computer and the count of computers.\n\n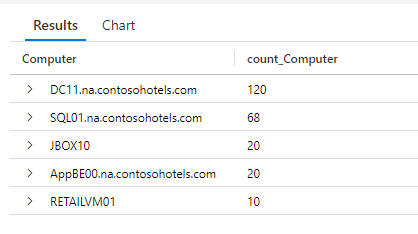\n\nClick on **Chart** to display the results as a chart.\n\n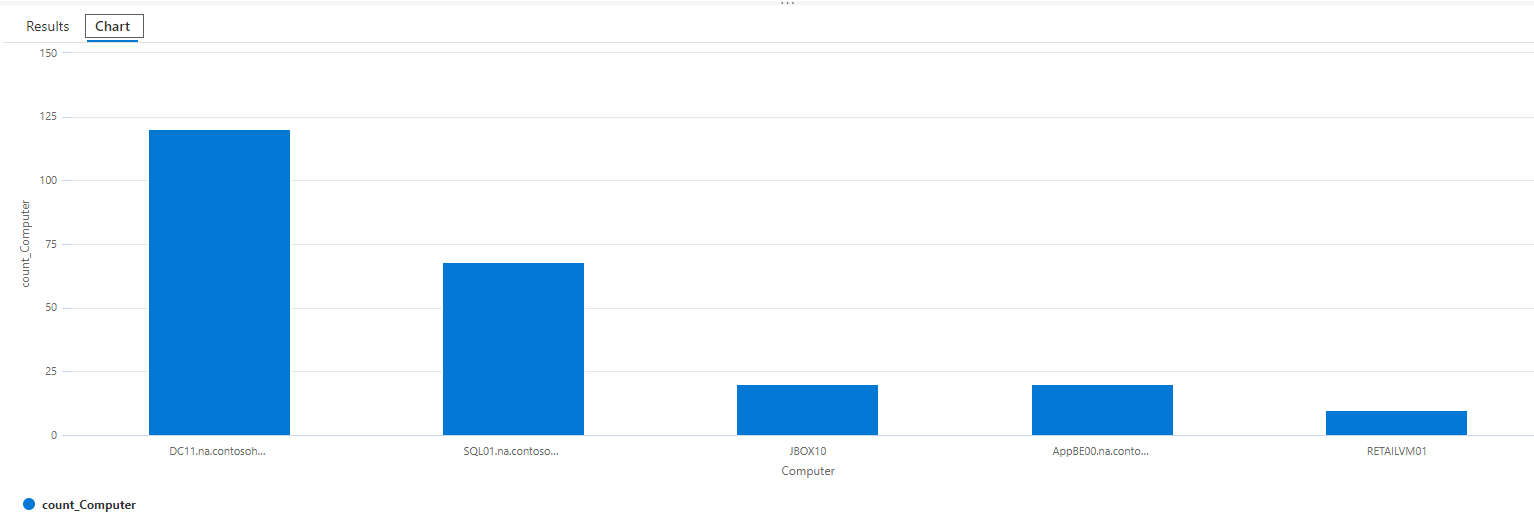\n\nOur lab is now completed.", "solutions_html": "Analyze virtual machine performance
\nWhen you log in to Azure with the provided credentials, you will find an empty resource group.
\n
This lab uses the Log Analytics demo environment, which includes plenty of sample data that supports the sample queries.
\nNavigate to the Log Analytics demo environment using the following URL.
\nhttps://portal.azure.com/#view/Microsoft_Azure_Monitoring_Logs/DemoLogsBlade
Construct a log analytics query that returns the following information:
\nCopy and paste the log analytics query and click on Run by selecting the whole query.
\nPerf\n| where TimeGenerated > ago(1h)\n| where (CounterName == \"% Processor Time\" and InstanceName == \"_Total\")\n| project TimeGenerated, Computer, CounterValue\n| summarize avg(CounterValue) by Computer, bin(TimeGenerated, 1m)\n| where avg_CounterValue > 100\n| render timechart
To view the results in a graph, select Chart on the results pane. Notice that there are various options for working with the chart, such as changing it to another type.
\n
Click on Results to view query results in a table organized by columns and rows.
\n
Construct a log analytics query that returns the following information:
\nCopy and paste the log analytics query and click on Run by selecting the whole query.
\nsearch in (Event, SecurityEvent) \"Antimalware\"\n| summarize count(Computer) by Computer\n| top 10 by count_Computer desc nulls last
The result will provide the details about the computer and the count of computers.
\n
Click on Chart to display the results as a chart.
\n
Our lab is now completed.
", "flags": [], "min_points_to_pass": null, "access_type": "web", "user_status": "unstarted", "user_lab_status": null, "user_status_modified": null, "user_flags": [], "global_running_session": null }